TRANSMISSION // 2611.10817v1
Can quantum key distribution stay secure when devices remember?
Source published
A new entropy-accumulation analysis incorporates finite memory in both quantum-key sources and detectors, then combines the two for BB84. Its detector model still requires disabling detectors and discarding affected rounds.
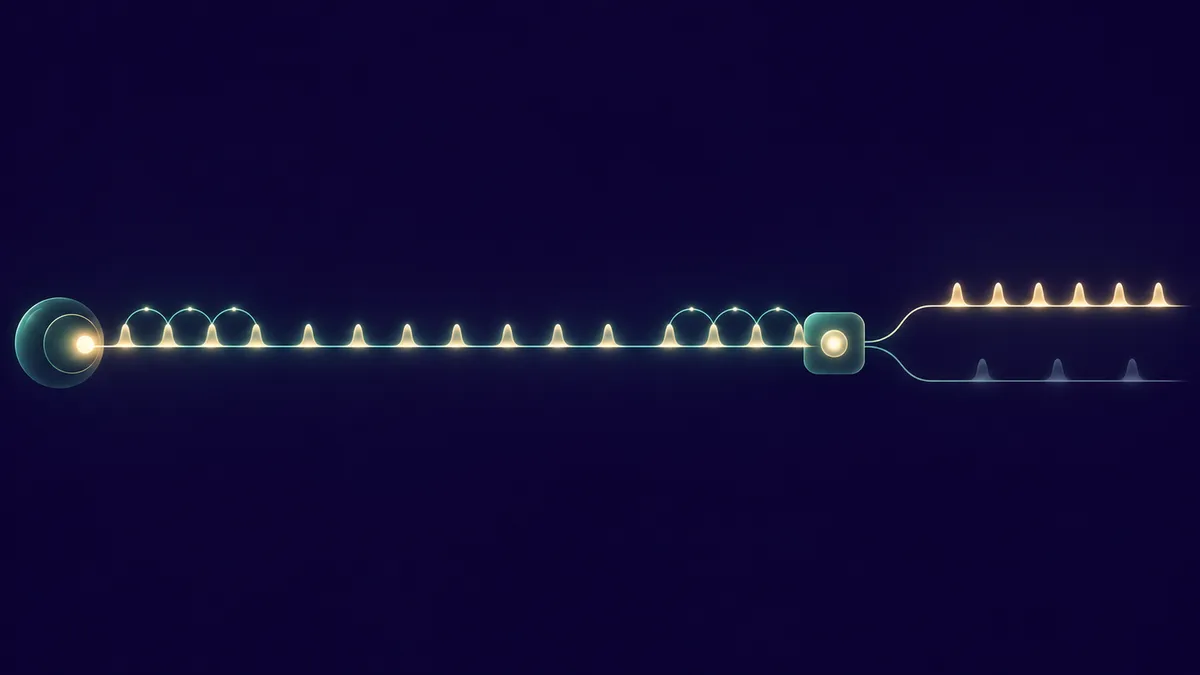
Quantum key distribution promises secret keys, but many security proofs assume Alice’s source and Bob’s detectors act independently from one round to the next. Real devices can remember: a source may emit a pulse influenced by recent settings, while a detector may stay inactive or become more likely to click after a detection. Devashish Tupkary and Amir Arqand adapt the marginal-constrained entropy accumulation theorem (MEAT) to account for certain kinds of both effects at once. Their work supplies a proof framework and an illustrative BB84 rate calculation—not a complete security certification of a particular device.
When one round affects the next
A security proof for quantum key distribution (QKD) must account for what an eavesdropper could learn, even when the equipment is imperfect. A common challenge is that many analyses treat each round as independent. But a source can produce a pulse based on recent setting choices, and a detector can have afterpulsing or dead time after a click. If the devices carry effects from one round into another, can a finite-key security proof still be made?
Tupkary and Arqand extend the marginal-constrained entropy accumulation theorem (MEAT), a tool for bounding how much secret information remains after many rounds. MEAT turns a multi-round protocol into a sequence of smaller, single-round optimizations. The authors’ central move is to represent memory explicitly, then reduce the analysis to versions of those familiar single-round calculations. Their results retain support for announcements made during the protocol and for tradeoff functions that can adapt to earlier public outcomes.
Making detector memory visible
A detector’s internal state is not automatically harmless to hide inside a proof: if its memory depends on the exact previous click pattern, giving that memory to the eavesdropper could reveal information about Bob’s outcomes. The authors therefore impose a concrete restriction. When detector effects may persist for a finite number of rounds after a click, all detectors must be switched off during those rounds. The affected rounds are marked with a special discard symbol and do not contribute key bits.
This rule lets the proof track a coarse description of memory—whether a relevant recent detection occurred—without needing the exact private click history. Public announcements must also indicate which memory-dependent behavior applied, so the entropy bound can distinguish the cases. This is a proof-compatible model, not a claim that arbitrary detector memory is covered. In particular, even weak correlations still trigger the prescribed shutoff and discarded rounds; finding a proof that uses such rounds when the effect is weak remains open.
Turning source correlations into blocks
For the source, the paper allows independently chosen settings but permits the state prepared in a round to depend on the current setting and a finite number of preceding settings. The authors handle this by splitting rounds into interleaved groups. They condition on settings in the other groups; that restores a product structure within blocks, where MEAT can be applied. The resulting bounds for the interleaved groups are then combined.
That reduction has a cost. Combining groups changes the Rényi-entropy parameter used in the security bound, and the single-round relaxation can give the eavesdropper additional later-round source “shield” systems. The authors retain a blockwise version as well as the more numerically practical single-round form; the latter is not necessarily tight. For longer-lived correlations, one could truncate the memory only if the difference between the real and truncated models is separately bounded.
A joint framework, with boundaries
The detector and source arguments can be combined, and the paper also describes iterative stopping rules for entanglement-based protocols when the decision depends deterministically on public announcements and there is a fixed maximum number of rounds. The authors illustrate their framework with qubit BB84 key-rate calculations under correlated source and detector models. Their simulations use specified settings—including a source-correlation model and detector shutoff after clicks—and show that positive rates can remain under those assumptions. The plotted example is not a full security proof for a practical hardware implementation: the authors leave detailed hardware characterization and experimentally motivated parameter choices to future work.
The scope matters. Source settings are assumed independent, with state dependence limited to a finite history; detector effects are finite-memory and require switching off all detectors during affected rounds. The analysis does not resolve general quantum memory inside devices, nor does it remove the performance cost of discarding detector rounds. For unbounded correlations, truncation needs an additional trace-distance bound to transfer security to the actual devices. The paper is an arXiv preprint, not evidence of peer review. Its contribution is a way to put two important classes of memory effects into one finite-size QKD security analysis while making the remaining device assumptions explicit.
- quantum key distribution
- BB84
- entropy accumulation
- correlated imperfections
- finite-size security
- quantum cryptography
Related reading
Automatically matched by shared topic keywords. These links do not imply that the sources agree or establish a consensus.
Before quantum keys, Sweden’s fiber links need a checkup
Source published
Shared keywords: quantum key distribution
When a quantum key begins with incomplete clues
Source published
Shared keywords: quantum cryptography, quantum key distribution
Two parity checks can filter errors in paired-state quantum keys
Source published
Shared keywords: quantum cryptography, quantum key distribution