TRANSMISSION // 2611.10670v1
When a quantum key begins with incomplete clues
Source published
A three-basis quantum key experiment turns partial knowledge into a shared secret—and tests the idea with real photons.
What if a quantum measurement could rule out one possibility without telling you which of the others is true? A new quantum key distribution experiment uses that kind of partial knowledge: Alice and Bob each learn only part of the other’s encoding, then reconcile those clues into a shared key.
Quantum key distribution (QKD) aims to let two parties establish a secret key while making eavesdropping detectable. Many familiar protocols are designed so that, after they compare public information and discard some measurements, Alice and Bob retain matching key data. The Bridge protocol takes a different route: a retained measurement gives each party incomplete information about the other’s choice, and they must use public classical communication to turn the overlap into a common key.
The researchers demonstrate Bridge[2,3], a version using two-dimensional photon polarization and three mutually unbiased bases. “Mutually unbiased” means that measuring a state prepared in one basis using another basis yields outcomes with equal probabilities. In the idealized protocol, Alice and Bob announce their state bits, not their bases, and keep events where those bits differ. Under ideal transmission, that mismatch means their bases differed too. With three possible bases, knowing that the other person did not use one particular basis still leaves two possibilities. The sifted records therefore contain partial, rather than complete, information about each other.
The authors describe a simple reconciliation procedure: for each retained position, Alice publicly names one of the two basis labels she did not use. If Bob’s label is not the announced one, he can infer Alice’s label by elimination; otherwise the position is discarded. In the idealized accounting, this leaves an average of half a trit per index in this simple scheme. The paper says more efficient reconciliation is beyond this experiment and refers to future work; it does not demonstrate that more efficient procedure.
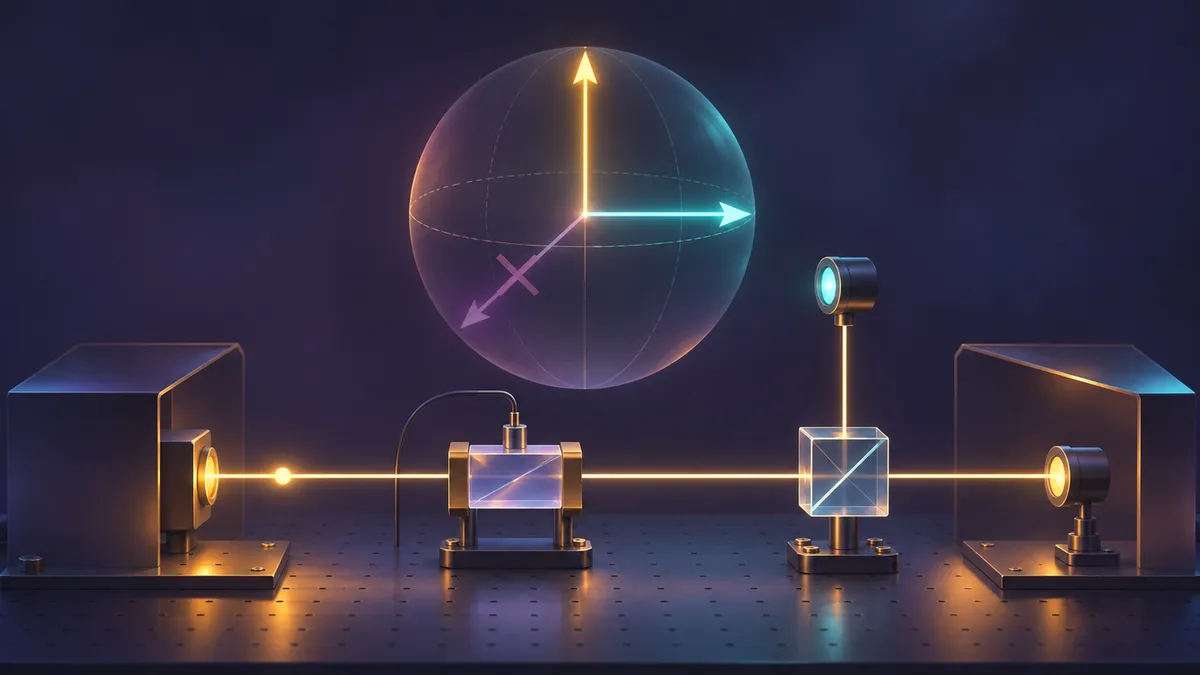
To test the protocol, the team prepared polarization states with an attenuated laser and used electro-optic Pockels cells—voltage-controlled elements that rotate polarization—to select states and bases. One Pockels cell selected among the three bases, and was used on the outbound and returning photon path. The light source emitted pulses at 780 nanometres and 76 million pulses per second, but the demonstration operated the modulation at 0.9 megahertz to limit acoustic ringing. The researchers used one in every 84 laser pulses for the changing-basis demonstration. A polarizing beam splitter and detectors recorded outcomes; the team matched detections to modulation settings afterward.
Tomography, a method for estimating a quantum state from repeated measurements, found an average angle of 88.6 ± 1.8 degrees between the prepared basis axes, close to the 90 degrees expected for unbiased bases. During protocol operation, the reported average state-tomography fidelity was 0.97 ± 0.02. These characterize the optical preparation and measurement; they are not by themselves a security proof.
The authors numerically estimate a secure-key rate under stated assumptions: optimal information reconciliation, a symmetric depolarizing channel, and a perfect single-photon source. In that model, the protocol’s threshold error rate is 5.75%. The measured quantum bit-error rate was 2.8 ± 0.9%, below that modeled threshold. From the same model and measured error, they report 0.26 ± 0.04 secure bits per sifted photon. After accounting for the experiment’s losses and its use of only one pulse in 84, they estimate a proof-of-concept output of 200 ± 20 secure bits per second. The apparatus did not implement a perfect single-photon source: it used weak coherent laser pulses, so that rate is not an end-to-end demonstration of security under realistic source imperfections.
This is an experimental demonstration of a protocol concept and a three-basis polarization-switching arrangement, not a deployed secure communications system. The authors note that photon-number-splitting attacks and the performance of the extended protocol need further study; decoy states or a single-photon source may be needed. They also point to higher switching rates and entangled-photon implementations as future possibilities. The result shows how partial information can be useful in a key-distribution design, while the gap between a modeled secure rate and a fully characterized practical system remains important.
- quantum key distribution
- quantum cryptography
- photon polarization
- mutually unbiased bases
- Pockels cell
- quantum communication
Related reading
Automatically matched by shared topic keywords. These links do not imply that the sources agree or establish a consensus.
Before quantum keys, Sweden’s fiber links need a checkup
Source published
Shared keywords: quantum communication, quantum key distribution
Can quantum key distribution stay secure when devices remember?
Source published
Shared keywords: quantum cryptography, quantum key distribution
Two parity checks can filter errors in paired-state quantum keys
Source published
Shared keywords: quantum cryptography, quantum key distribution
Quantum grid codes could extend direct secure messaging beyond 1,000 kilometres
Source published
Shared keywords: quantum communication
Waiting to measure can unlock an unbounded quantum communication advantage
Source published
Shared keywords: quantum communication